

OUR SERVICES
With NCO you have top-notch security experts using the most advanced tools monitoring and managing all of your systems, so you can sleep at night knowing you're protected. Learn below about key offerings in email and cloud protection, endpoint protection (EDR), and security information and event management (SIEM).
Schedule a DemoEMAIL & CLOUD PROTECTION
Email Threats Account for 95% of Attackers' First Foothold into a Company's Network.
That vulnerability only grows as more business operations move to the cloud through collaboration apps. Go beyond traditional security tools and choose NetCyberOps. We combine behavioral AI with highly trained security experts to provide the most comprehensive and responsive protection in the industry.
 SUPERIOR
99% reduction in phishing attacks reaching the inbox
 PROTECTION
Ransomware, account takeover, BEC, supply chain attacks
 FULL-SUITE
Security for all your collaboration apps
USER ANOMALY DETECTIONS
Suspicious Login Identification: Stopping threat actors from accessing victim accounts from different geographic locations, utilizing different computer and web browser fingerprints.
Business Email Compromise: Immediately identify internal email accounts that have been compromised and disable the accounts before they are used to distribute malicious emails or files.
Assisted Rule Removal: Malicious inbox rules remain a threat actor's tool of choice for data exfiltration and obfuscation. MDR for Google Workspace and O365 introduces an Assisted Remediation for malicious inbox rule removal with only one click.
ADDITIONAL
EMAIL PROTECTION FEATURES:
| 01 | Integrate next-gen email directly with O365 and Google Workspace. |
| 02 | Monitor email, Sharepoint, Google Drive, OneDrive, Teams, Slack, and several other collaboration tools for malware and suspicious links. |
| 03 | Manual investigation of all reported phishing emails and necessary remediation actions. |
| 04 | Analysis of email content for common financial/phishing language, alerting MDR team to investigate. |
- 01
Integrate next-gen email directly with O365 and Google Workspace.
- 02
Monitor email, Sharepoint, Google Drive, Onedrive, Teams, Slack, and several other collaboration tools for malware and suspicious links.
- 03
Manual investigation of all reported phishing emails and necessary remediation actions.
- 04
Analysis of email content for common financial/phishing language, alerting MDR team to investigate.
Fully Managed Detection & Response
At the core of NetCyberOps is our ability to fully manage endpoint security tools across your entire environment. We monitor these endpoints and can investigate, validate, and mitigate threats remotely, combining industry-leading tools with world-class talent to protect your business.
98%
reduction in alert volume
10X
improvement in threat detection
40%
average improvement in program efficacy
90%
increase in identified threat containment
NEXT-GEN ANTI-VIRUS AGENT USING AI MALICIOUS BEHAVIOR DETECTION
Endpoint agents log all activity on each device to enable comprehensive investigations.
Real-Time Security Dashboard for customers to monitor MDR team activity and security related data.
ADDITIONAL ENDPOINT DETECTION & RESPONSE FEATURES:
| 01 | Continuous monitoring and response to generated alerts. |
| 02 | Daily threat hunting for advanced threats. |
| 03 | Real-time reporting of all SentinelOne and MDR team activity to partner and customer via NCO dashboard. |
| 04 | Real-time reporting of all EDR events and MDR team activity to partners and customers via NCO unified dashboard. |
| 05 | Complete management of EDR tools. |
- 01
Continuous monitoring and response to generated alerts.
- 02
Daily threat hunting for advanced threats.
- 03
Real-time reporting of all SentinelOne and MDR team activity to partner and customer via NCO dashboard.
- 04
Real-time reporting of all EDR events and MDR team activity to partners and customers via NCO unified dashboard.
- 05
Complete management of EDR tools.
SECURITY INFORMATION & EVENT MANAGEMENT (SIEM)
Fully Protected, Fully Managed
NetCyberOps utilizes next-gen SIEM technology that provides state-of-the-art threat detection across hundreds of log types. AI capabilities create baseline activity for each unique user and asset and will alert the NCO team if irregular or suspicious behavior is detected.
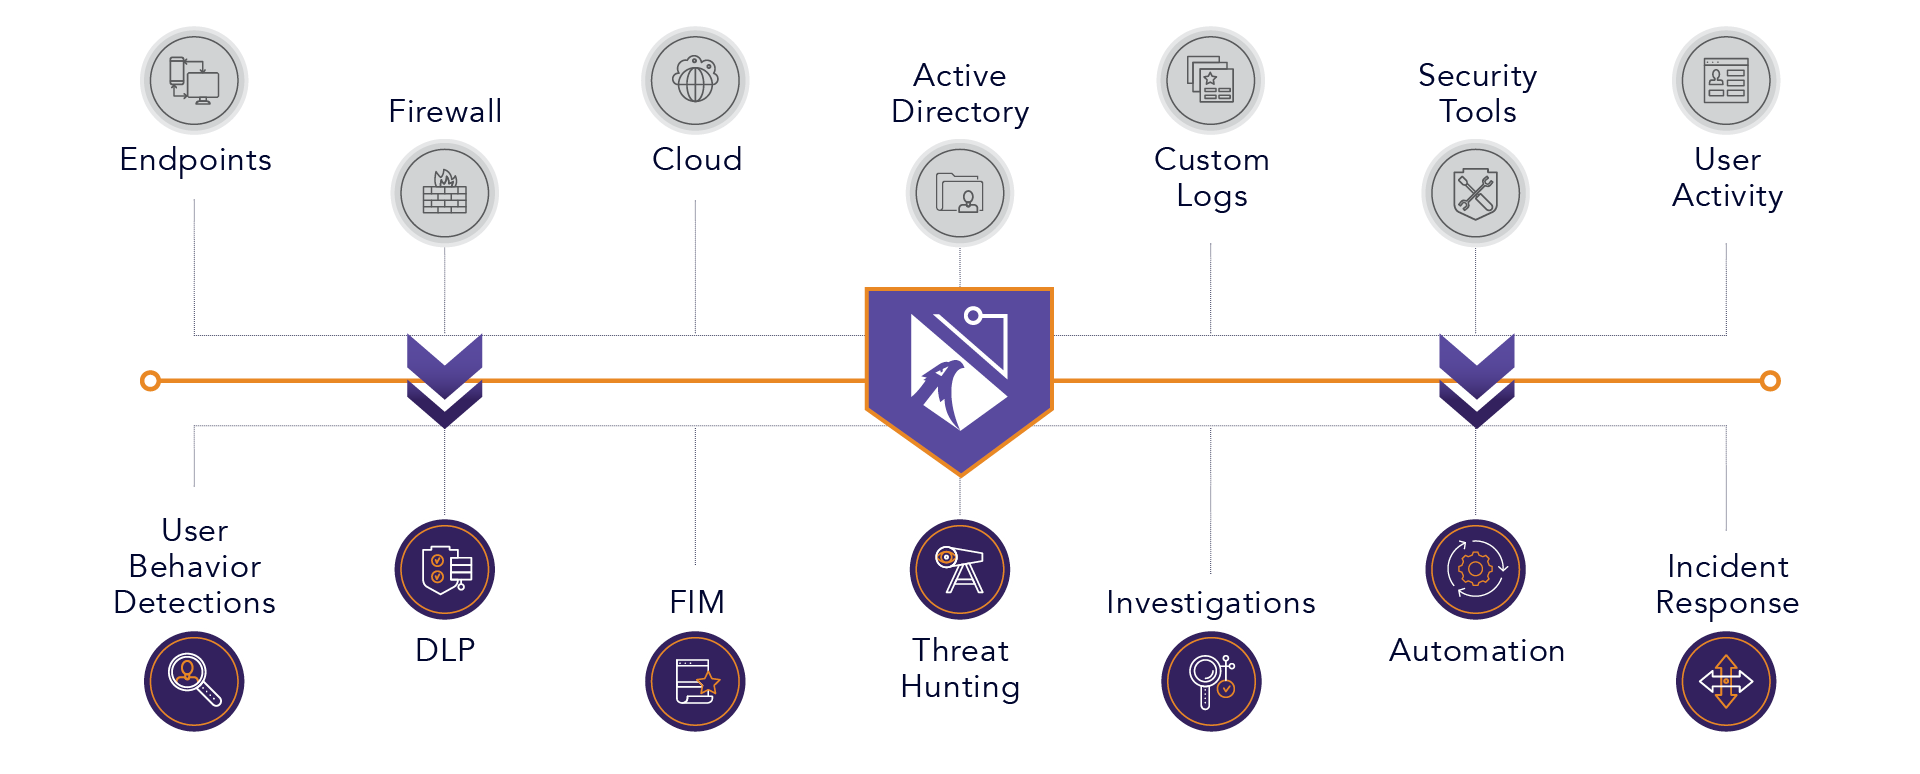
NETCYBEROPS 24x7 MANAGED DETECTION AND RESPONSE WITH SIEM
When approved, NCO MDR team will take response and remediation actions utilizing the SIEM agent's capabilities. The MDR team will also utilize remote shell capabilities for incident response for customers with NCO's managed EDR services.
NCO's SIEM will create a baseline for each user's behavior and activity over the first 2 weeks of deployment. Any activity that falls outside of the baseline will be heavily scrutinized and create investigations for the MDR team to review.
NCO's MDR team continuously tunes and updates signatures related to suspicious user activity. Once user behavior is verified, NCO will exclude the specific activity to avoid repeat alerts.
Combining SIEM with EDR and Email Security enables the NCO MDR team to have 100% visibility into a customer's network and allows the team to investigate, validate, and fully remediate threats.